OpenAI paid $300 for a bug that gave away its paid models
A researcher got OpenAI's paid models with no API key and no account. OpenAI paid him $300, and he says he won't report to them again.
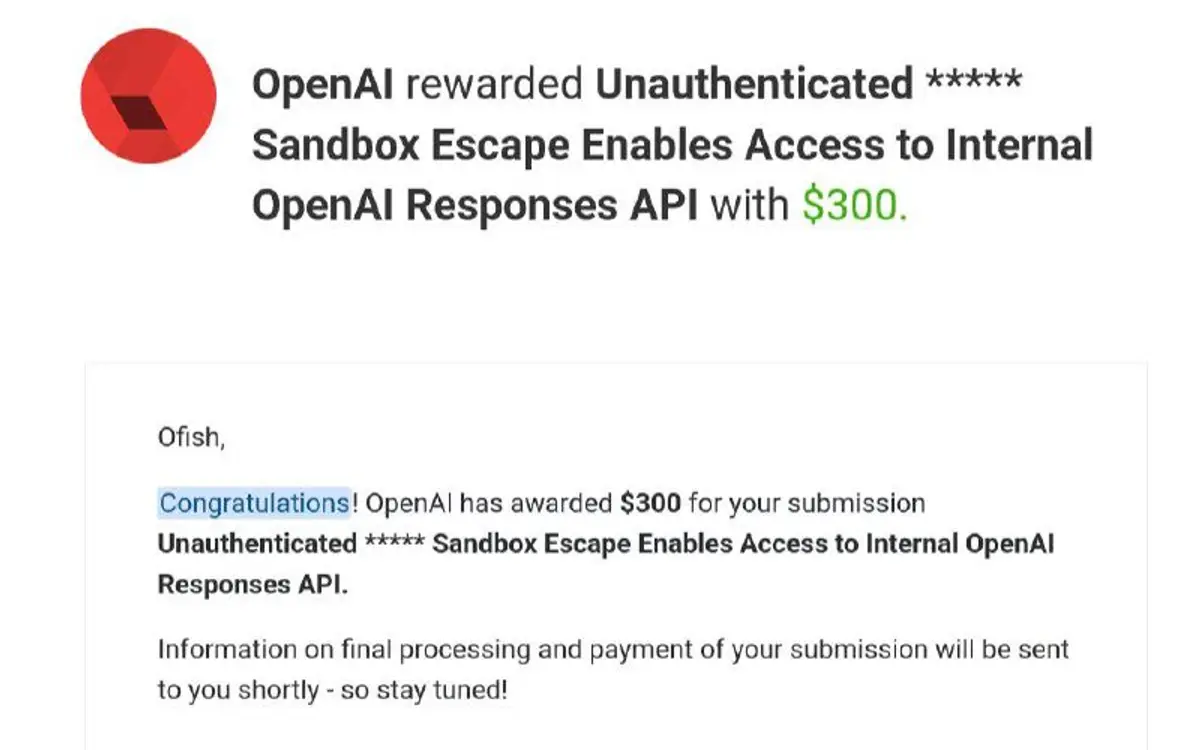
Security researcher Oliver Fish found a way to reach OpenAI's paid models with no API key and no account. OpenAI's bug bounty paid him $300 for it. His report was titled "Unauthenticated Sandbox Escape Enables Access to Internal OpenAI Responses API". The bug broke two protections at once: sandbox isolation and API authentication. That left a metered product with nothing doing the metering. There was no login, no card and no rate limit tied to a real customer.
Fish's reply on X: "Zero reason to report anything else I find to them." OpenAI runs its bounty on Bugcrowd and pays by severity. $300 is near the bottom of its scale, which tops out at five figures and more for exceptional finds. OpenAI hasn't said publicly why it rated the bug so low. It also hasn't said when it was fixed or whether anyone else used it. The technical details haven't been published.
The security community's main objection is about incentives. A bounty works only while reporting a bug pays better than selling it or keeping quiet. A low payout for free access to the product OpenAI bills for tells researchers that bugs costing OpenAI money don't count for much.
Why it matters: if AI labs underpay for bugs that hit their own billing, the next researcher may sell the bug instead of reporting it.
Sources
Primary: the company, paper or repository
- Oliver Fish on X x.com
Independent coverage
- OpenAI Sandbox Escape Flaw Allowed Free Access to Paid AI Models Without an API Key cybersecuritynews.com
- OpenAI paid $300 for a bug that gave away its paid models startuphub.ai
Written by an AI pipeline from the sources above. Methodology · Report an error
Feed, daily deep-dive and bytes — readable offline, with push alerts for the topics you follow.