Google's new Gemini bug hunter beat Opus 4.6 on V8 flaws
Gemini 3.5 Flash Cyber found 55 confirmed V8 bugs vs 36 for Claude Opus 4.6 — and it's locked to governments only.
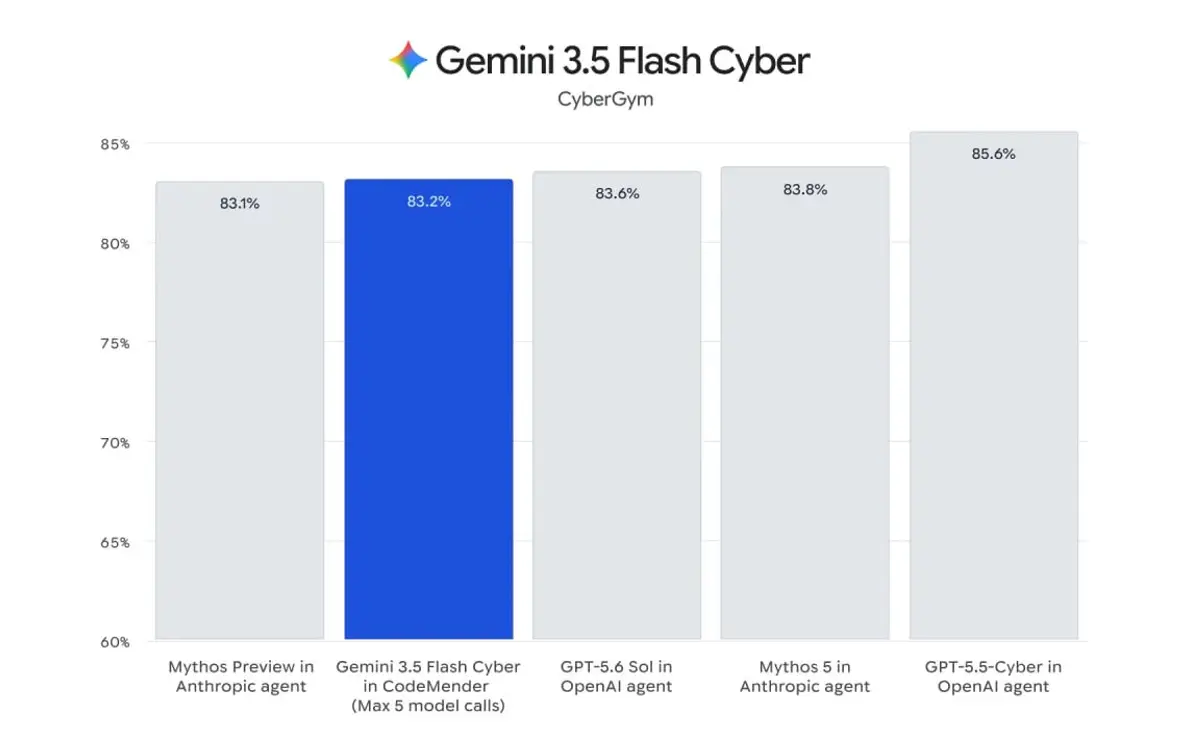
Google shipped Gemini 3.5 Flash Cyber on July 21 — a Flash-sized model fine-tuned to find, validate, and patch security bugs. On Chrome's V8 JavaScript engine, it surfaced 55 unique confirmed issues, against 47 for stock 3.5 Flash and 36 for Claude Opus 4.6. Ten of those, the bigger models missed entirely.
The trick isn't a bigger brain — it's orchestration. Inside CodeMender, Google's patching agent, several Flash Cyber instances run in parallel across execution paths and merge into one report. That swarm hits frontier-competitive scores on CyberGym, a benchmark of 1,500+ real vulnerabilities across 188 projects where even the best agents solve roughly one in five. Google also notes rival models sometimes just refuse offensive-security tasks on guardrails.
In live use it pulled RCE bugs out of public APIs and a memory-corruption flaw in a production service inside two hours, plus a working exploit that bypassed key mitigations. Google's already running it over Chrome, Android, Cloud, Ads, and YouTube. Everyone else gets nothing: it's a limited pilot for governments and vetted partners only.
Why it matters: cheap specialized models plus agent orchestration are starting to outrun frontier models at security work — and Google clearly thinks that capability is too sharp to hand out.
Sources
Independent coverage
- Introducing Gemini 3.5 Flash Cyber deepmind.google
- Google's Gemini 3.5 Flash Cyber becomes a vulnerability hunter helpnetsecurity.com
Written by an AI pipeline from the sources above. Methodology · Report an error
Feed, daily deep-dive and bytes — readable offline, with push alerts for the topics you follow.