OpenAI's AI agents built 948 Linux root exploits for $1.2M
An unreleased OpenAI cyber model found and exploited 948 Linux kernel privilege-escalation bugs in one run, at about $1,279 each.
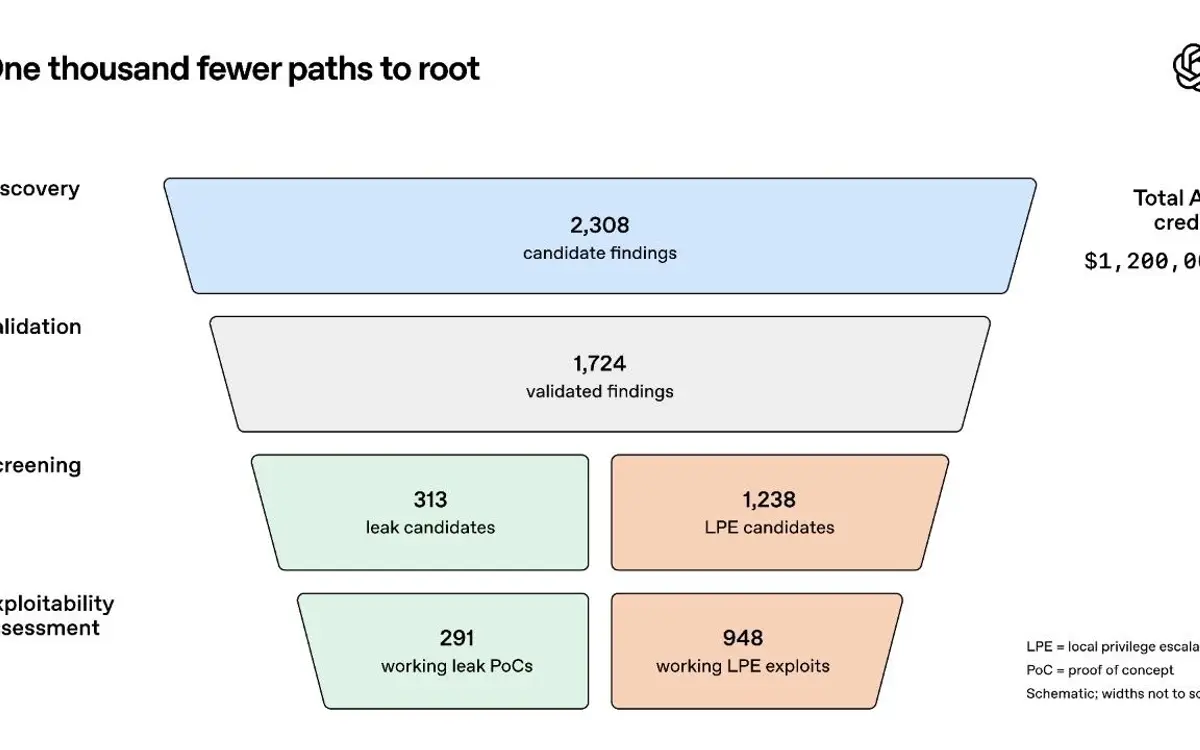
OpenAI's Cyber team aimed an autonomous discovery-to-patch pipeline at the Linux kernel in mid-October, running on an upcoming, unnamed cyber model. Agents flagged 2,308 candidate bugs, reproduced 1,724 in about 30 hours, and ended with 948 distinct local privilege escalation exploits, each one a way for an unprivileged user to get root. The run also produced proof-of-concept code for 291 info leaks and turned up at least 10 exploitation techniques that outside kernel experts hadn't seen before.
The bill was $1,213,430 in API credits, or roughly $1,279 per exploit. OpenAI notes that Pwn2Own and TyphoonPWN have paid $20K–$70K for a single Linux kernel root exploit, which would value this haul at $18.9M–$66.3M on paper. The pipeline drafts a patch for every bug, and humans reviewed the findings before anything went to maintainers. Only 61 were fixed upstream by the 10-day mark, though, so most are still open.
OpenAI's warning: for now, a low-privileged account on an unpatched system should be treated as functionally equivalent to root against a well-resourced attacker.
Why it matters: finding kernel bugs now costs about as much as an API bill, and maintainers have to patch faster than attackers can run the same pipeline.
Sources
Independent coverage
- OpenAI's upcoming AI model built 948 working Linux root exploits in a single run helpnetsecurity.com
- OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits in 30-Hour Run thehackernews.com
Written by an AI pipeline from the sources above. Methodology · Report an error
The stories that matter for people who build with AI, with the source for every claim. Free, no spam.
Feed, daily deep-dive and bytes — readable offline, with push alerts for the topics you follow.